

CYBERSECURITY SEO AGENCY
GrowPad is a cybersecurity SEO agency for security software vendors, managed security providers, and security platforms. Our SEO, GEO, and AEO work helps your product become the answer security teams find in Google, ChatGPT, Perplexity, and AI Overviews. We measure the results in demos, SQLs, and pipeline.

MQLs in 5 months
Monthly LLM mentions in 90 days
Five-star reviews on Clutch


Security buyers research quietly in Google and AI assistants for weeks before they contact a vendor. GrowPad’s Trajectory® methodology concentrates the first 90 days on the queries and AI prompts where security teams build their shortlist.
We map comparison and alternative queries for your security category, then build or improve the pages that answer them.
You get: Visibility when teams compare vendors, turning search demand into demo requests.
We build pages showing how your product supports SOC 2, ISO 27001, and NIS2 requirements, without overstating what software can certify.
You get: Leads from teams with deadlines, budgets, and a clear need for a solution.
Our GEO, AEO, and LLMO work tracks your platform across buyer prompts and uses cited sources to guide content and outreach.
You get: Your platform on the AI-generated shortlist before security teams visit vendor websites.
We build evergreen hubs for the threats your product addresses, so timely updates can rank on pages with existing authority.
You get: Your brand in front of buyers when vulnerabilities and incidents turn urgency into budget.
We assess product, solution, and use-case pages in the first weeks, then prioritize fixes for those with commercial potential.
You get: Faster results from existing pages, often before new content goes live.
We set baselines for ACV, sales cycle length, close rate, and lead volume, then track organic touchpoints throughout the cycle.
You get: A clear view of how organic and AI search influence pipeline, even when deals close a quarter later.
Cybersecurity buyers are technical, skeptical, and risk-averse by profession. That changes what content earns trust, how long conversion takes, and how search performance should be measured.
CISOs, security architects, and SOC leads see vendor hype every day. Content built on fear, vague claims, or generic threat statistics loses credibility fast. Pages must show real detection logic, deployment details, and integration specifics. Otherwise, they earn neither trust nor demos.
SIEM, XDR, SASE, CNAPP, and zero trust often describe overlapping capabilities. Buyers may search for the problem, while vendors name the category. We map how your ICP actually describes the problem, then align page architecture to that language rather than your positioning deck.
Security content must be technically correct and reviewed by practitioners. It also has to explain threats without publishing details that help attackers. We build content with your security experts and keep claims inside what your product actually does.
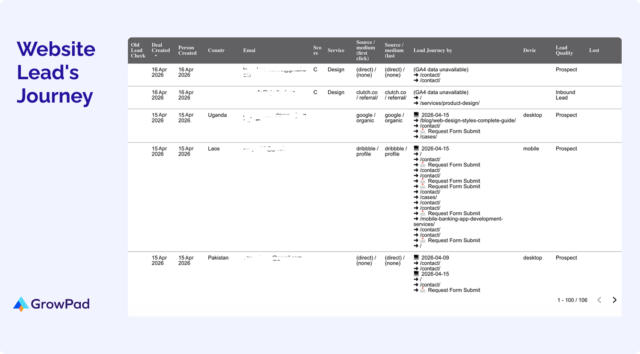
Security teams check peer review platforms, analyst coverage, and practitioner communities before booking demos. AI assistants often cite the same sources. External mentions in the right places matter as much as your own pages.
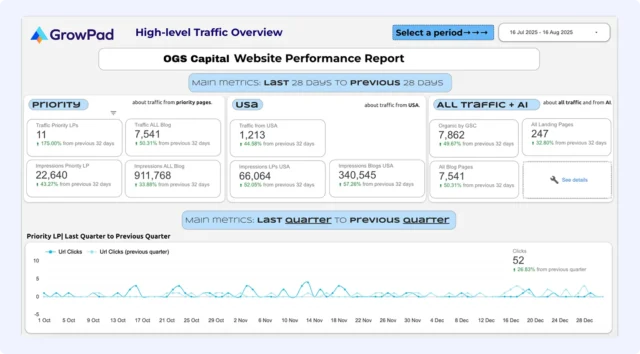
A security deal can involve IT, compliance, procurement, and the board. Last-click reporting rarely credits the search visit that started the evaluation. We define attribution rules before work begins, so reporting reflects how your deals actually close.
A strategy call shows where your product stands in Google and AI search against the vendors your buyers compare you with.
GrowPad owns the agreed scope of organic and AI search as a channel. We deliver strategy, execution, and measurement as a partner, not as a task vendor.
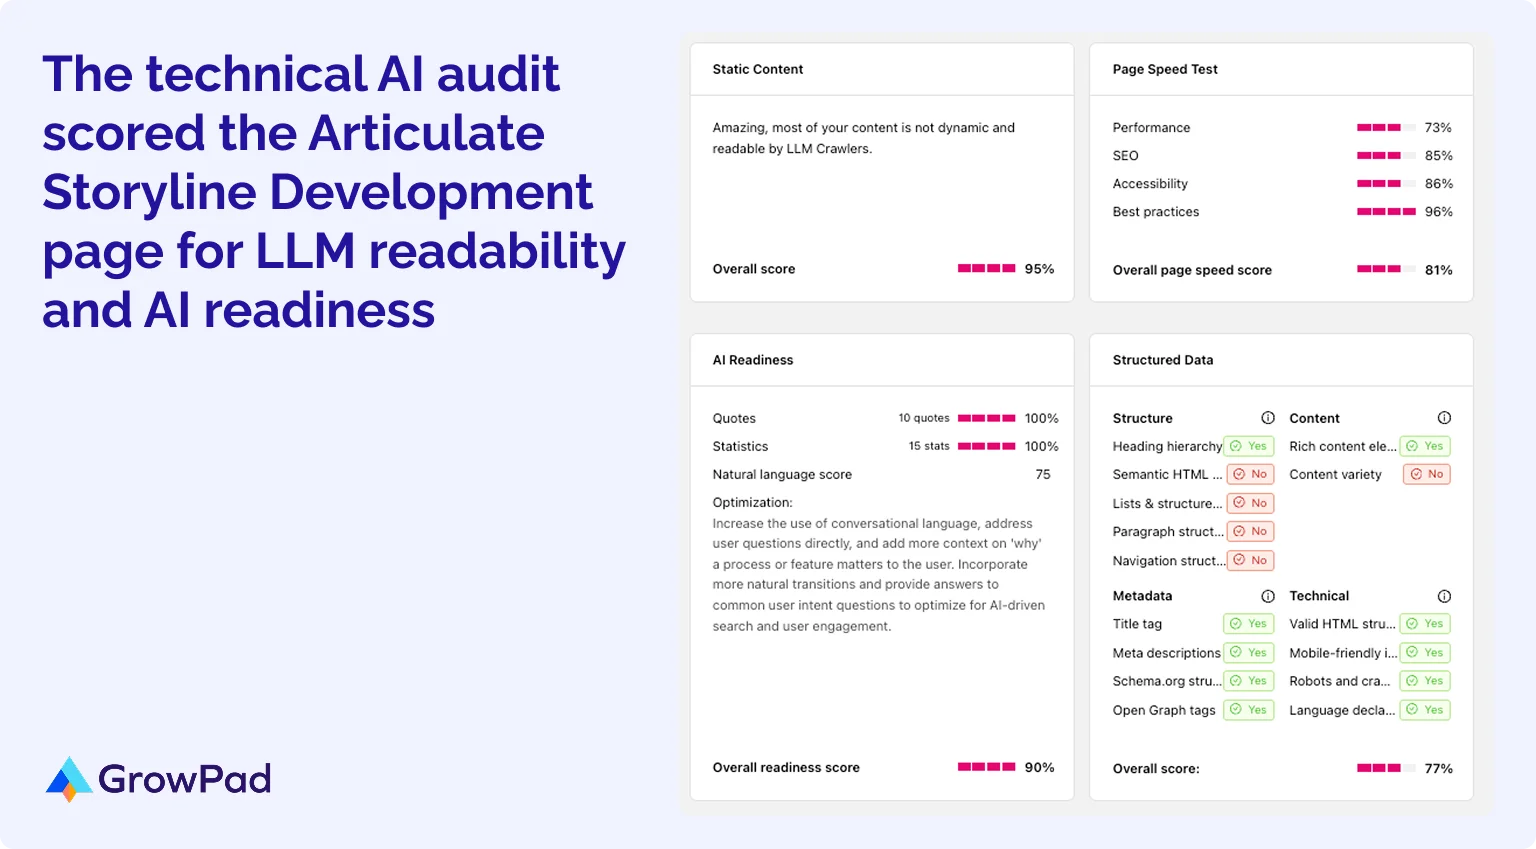
We review rankings, technical health, content gaps, backlink profile, and presence in AI answers for your security category. The audit sets your performance baseline and prioritizes the first quarter. Learn more about our SEO audit process.
You get: A clear list of what blocks demo requests today and what to fix first.
You receive a roadmap of which shortlist, compliance, threat, and integration pages to own first, and how to sequence content and authority work. We update it monthly as ranking and AI visibility data comes in.
You get: A budget spent on pages closest to pipeline, not on generic security news.
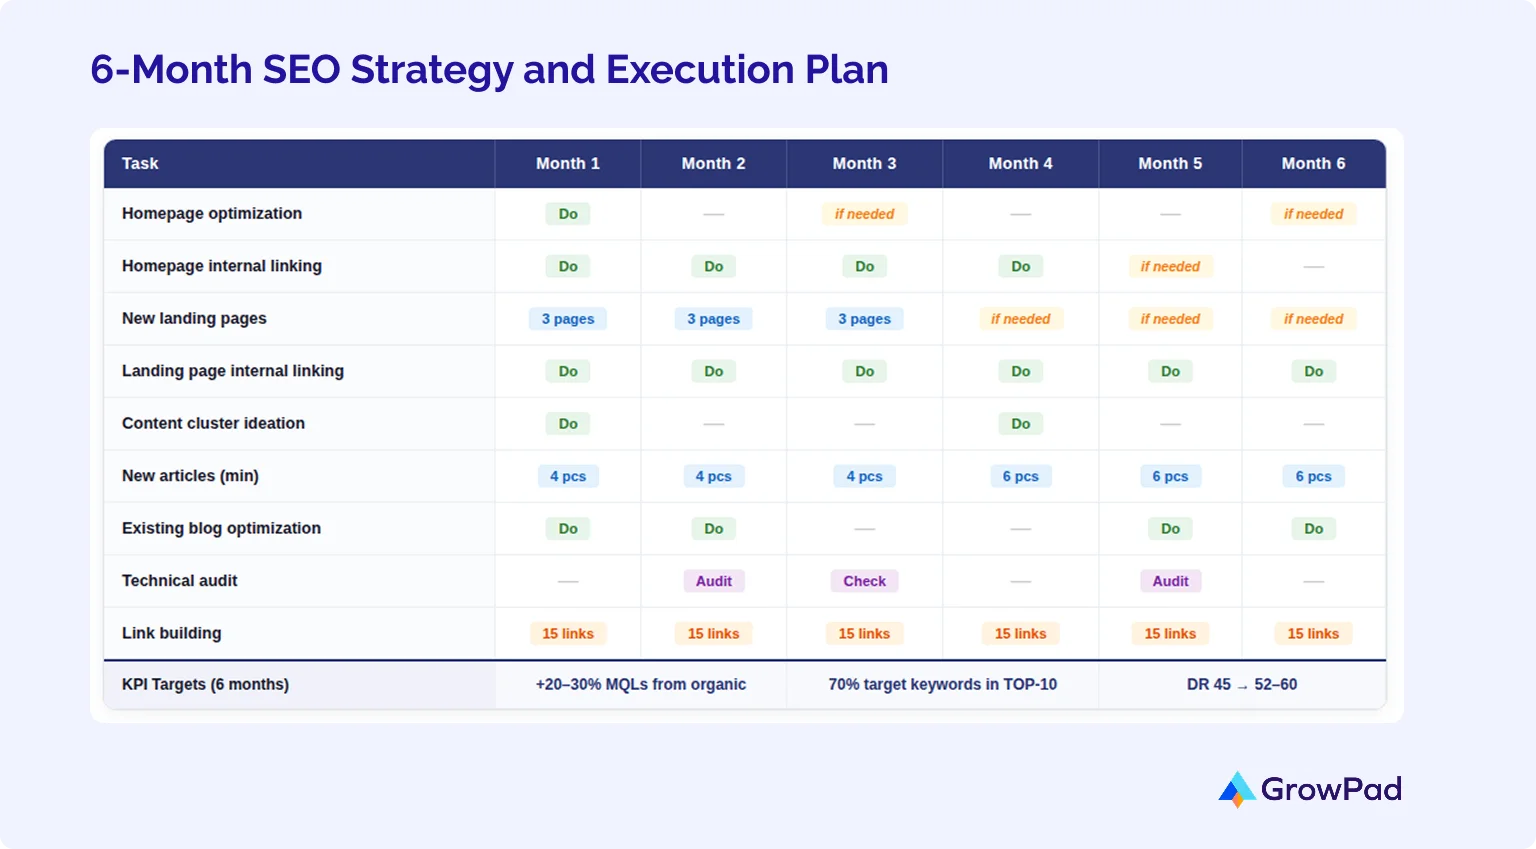
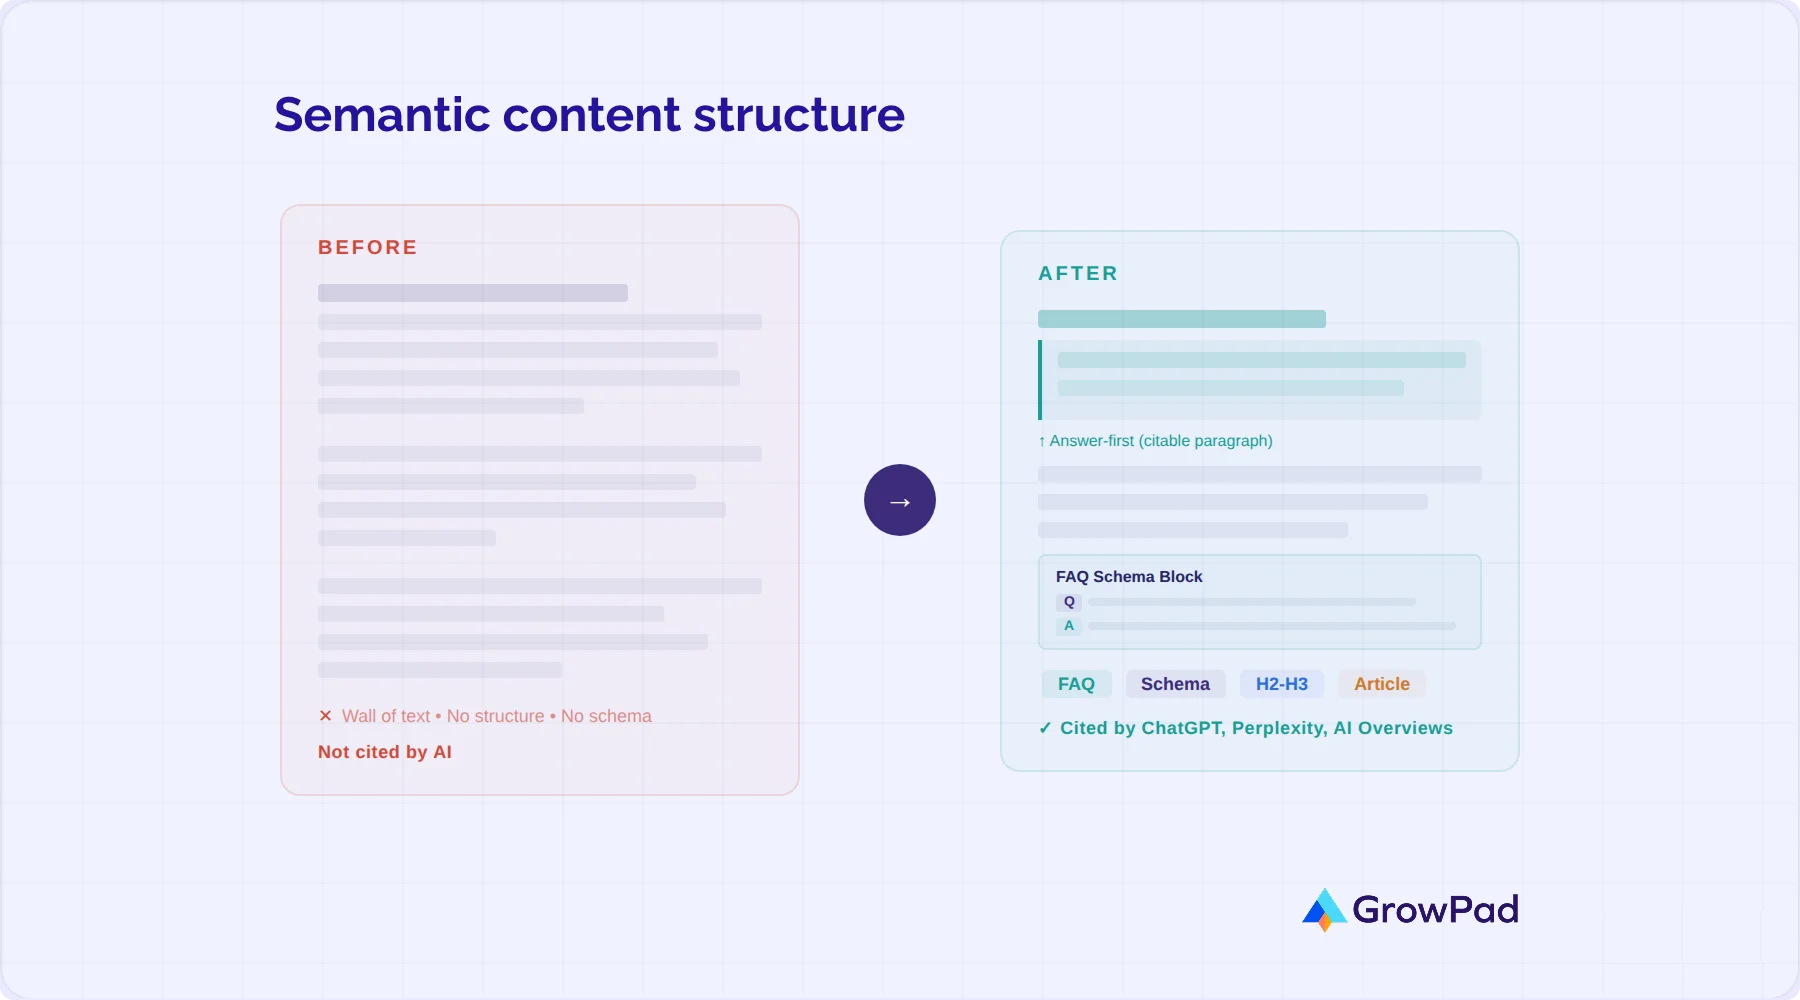
We write product, solution, compliance, comparison, and alternatives pages for security teams at the evaluation stage. Your experts review every technical claim before publication. Growth and Accelerate packages include publishing into your CMS. Starter includes recommendations plus one page implemented. See how we approach content marketing for tech products.
You get: Pages that practitioners trust and that move evaluators toward a demo or proof of concept.
We secure editorial placements on relevant security and IT publications, “best cybersecurity tools” listicles, and software directories. Outreach prioritizes the sources ChatGPT, Perplexity, and AI Overviews already cite for your category. Every placement is approved before going live. See our link-building and AI-citation service for the process.
You get: Mentions in the sources security buyers and LLMs already trust.

We track your share of voice across buyer prompts and compare it with named competitors. We then structure content and entity signals so LLMs connect your product to specific threats, environments, and compliance needs. Our GEO and AEO services describe the full workstream.
You get: A measurable share of voice against competing vendors in the AI answers your buyers read.

Rankings and traffic are diagnostics. The outcomes of working with a cybersecurity AI SEO agency below connect search work to revenue.
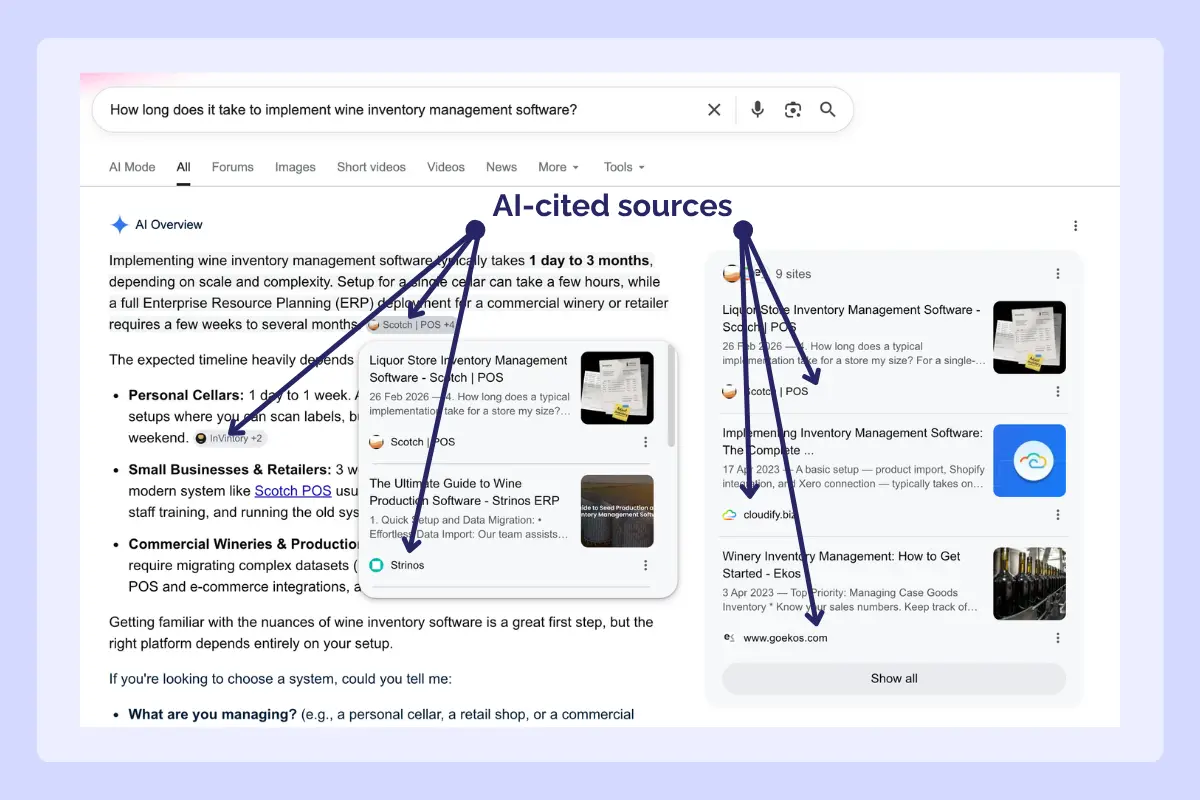
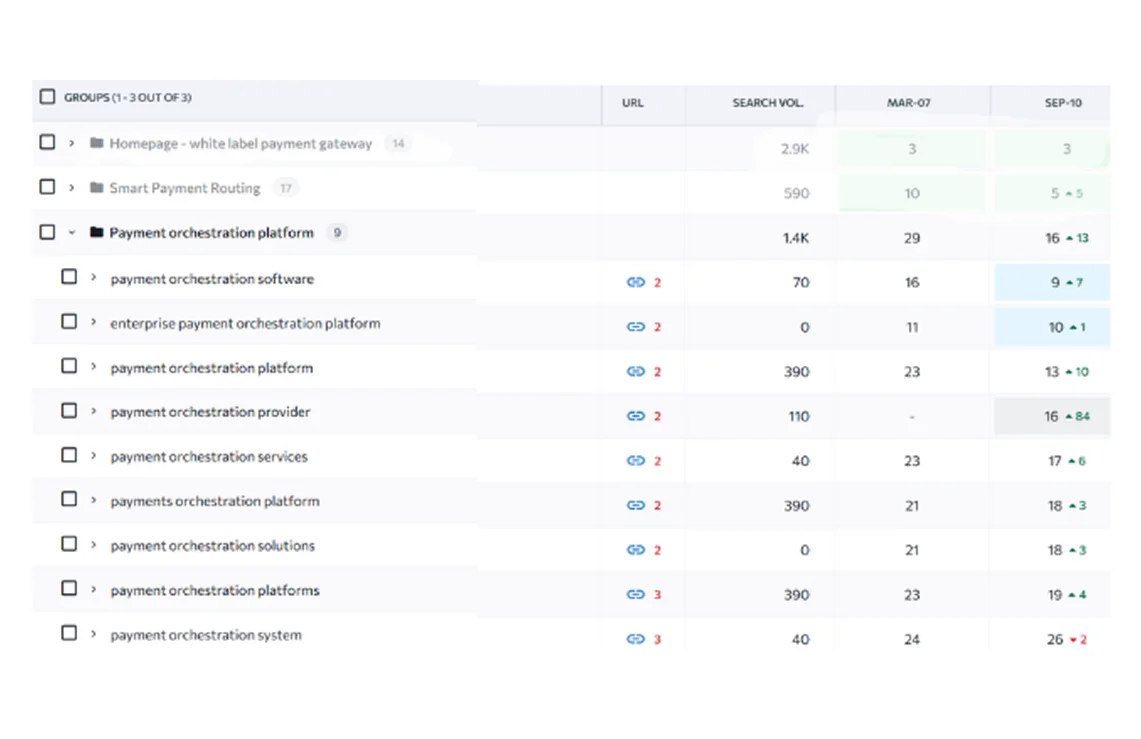
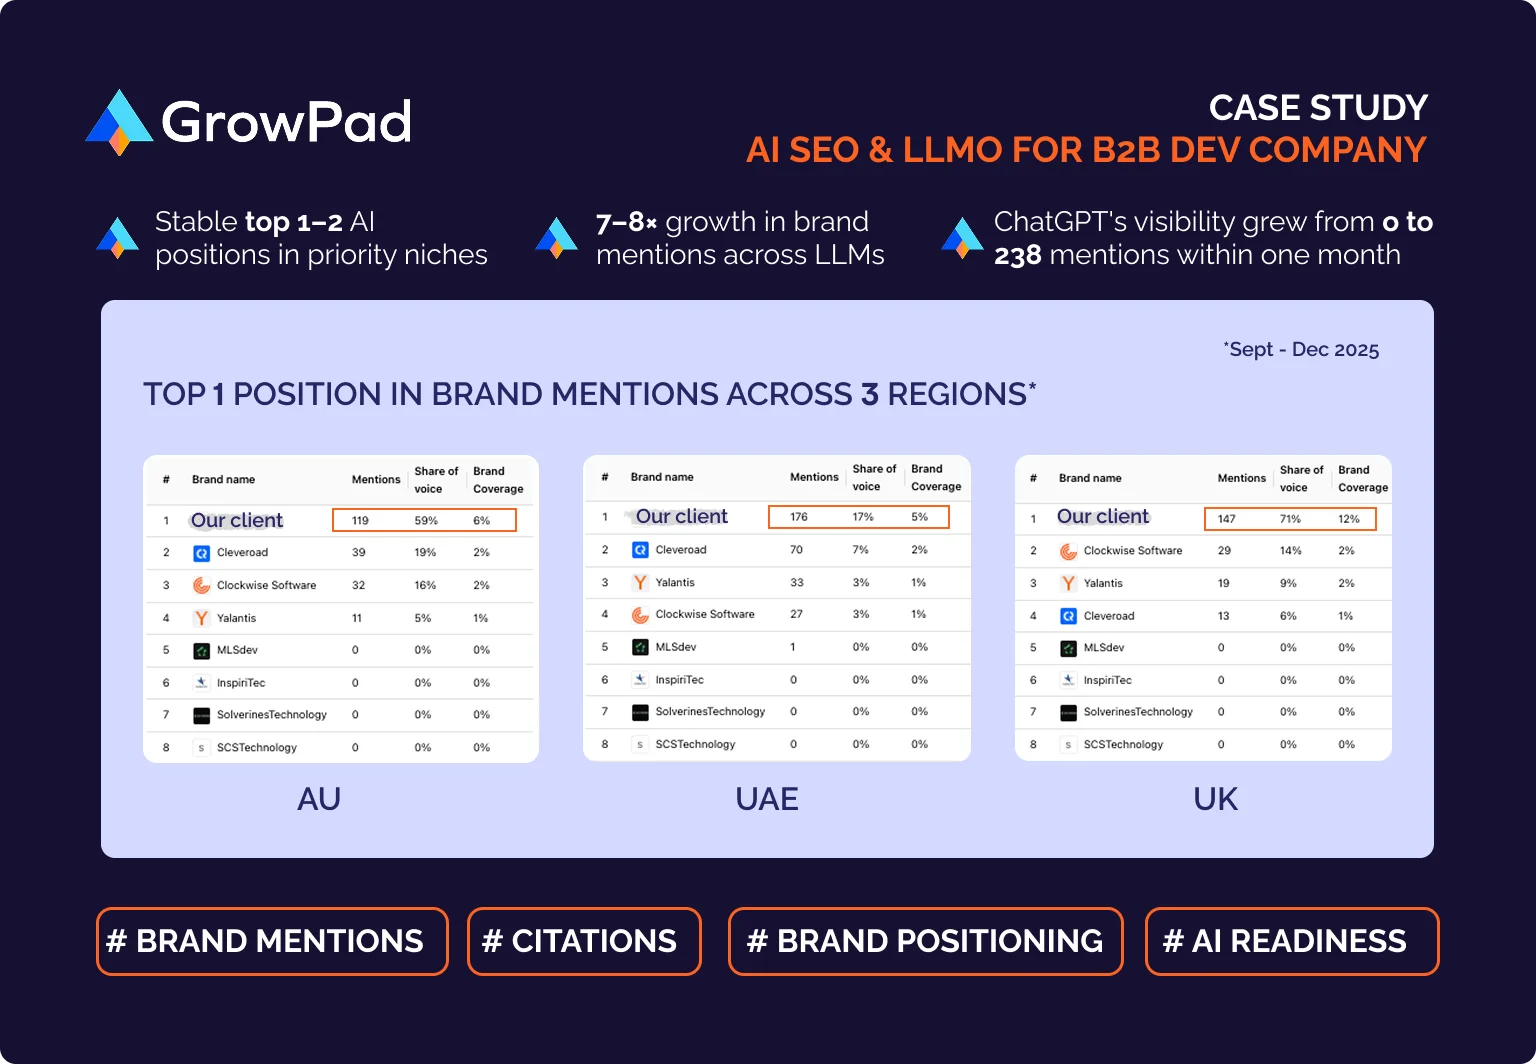
A custom software development company (NDA) working across logistics, real estate, and other complex technical domains came to GrowPad with strong classic SEO but no systematic presence in AI-generated answers. AI visibility was treated as an SEO byproduct, with no clarity on which niches could convert.
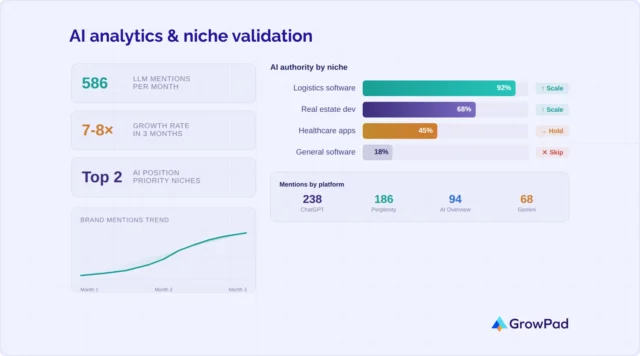
GrowPad concentrated the LLMO work on custom logistics software development as the priority niche and built entity signals across owned content and trusted third-party platforms. The team introduced AI-optimized content templates, published five listicles per month, and placed brand mentions on sources frequently cited by AI. Within three months, brand and domain mentions across LLMs grew 7–8×, from about 75 to 586 per month. The company moved from positions #5–6 to stable top 1–2 in ChatGPT, Perplexity, and Google AI Overview for priority niches.
Not sure where to invest next: SEO, content, or SaaS link building? Book a session with Oleksii to pressure-test your growth strategy. He’ll show you where your authority gaps are, which campaigns will compound fastest at your stage, and what to stop spending on.

Oleksii Andrusenko
Founder of GrowPad
In two years, we published over 100 articles, launched over 10 landing pages, and updated over 200 legacy pieces. This doubled our SEO traffic and increased MQLs by 1.5 times. The team was well-organized, quick to respond, and effective, which let us deal with problems quickly and keep making steady progress throughout the project.
Anna Umanenko, Head of Marketing, Onix-Systems


We will review your category, competitors, and AI visibility, then explain what is realistic at your stage.
A cybersecurity SEO agency builds strategy around how security teams evaluate vendors: shortlist queries, compliance requirements, threat-driven searches, and AI recommendations. Content must hold up under review by practitioners. GrowPad adapts its methodology to these security-specific buying patterns.
We work with security software vendors, managed security providers, and security platforms that have product-market fit. Both product-led and sales-led models are a fit. We are not a fit for pre-product companies or teams expecting results within 60 days.
GrowPad cybersecurity SEO programs start from $3,000 per month. Every engagement begins with a paid three-month Sprint that includes an SEO and AI visibility audit and strategy. Link placements and GA4 setup are quoted separately when needed.
Early ranking signals usually appear within 2 to 4 months. First SQLs follow once commercial pages rank and convert. Because security deals often run for months, their full revenue impact appears later than in shorter sales cycles.
Yes. Our GEO, AEO, and LLMO work tracks your product across buyer prompts in ChatGPT, Gemini, Perplexity, and AI Overviews. We then run outreach to the sources those answers cite. We report AI share of voice quarterly but do not guarantee citations.
We agree on conversion definitions and attribution rules at onboarding, including demos, proof-of-concept requests, and SQLs. We track organic touchpoints in GA4 and map them to your CRM. Quarterly reviews assess search’s influence on opportunities and closed revenue.
No. GrowPad focuses only on SEO and AI search. This lets us own the organic channel fully instead of spreading effort across unrelated channels.

We guide your ideal clients to you by blending SEO, GEO, and LLMO, as well as content briefs and link building into a cohesive inbound marketing strategy.
Growpad Digital Growth S.L.B26742650
Avinguda Goleta, 3, local 7, despacho 4, Alicante, Spain, 03540
Tel: +34624126313